
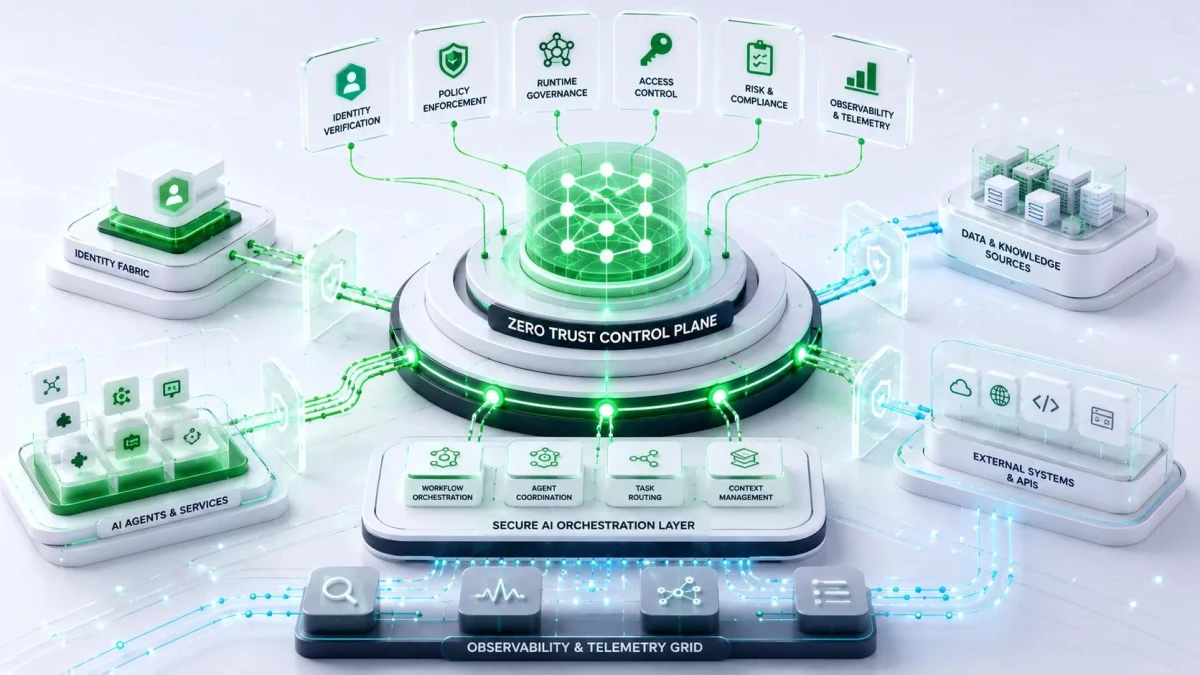
Here are the steps a security team can take:
- Take inventory of all agents. “Orphaned” agents with no clear owner violate zero trust from the start. Bleeping Computer
- Give each agent its own identity. 1Password says attestation lets an issuer bind an agent’s workload to an identity automatically, without human intervention.
- Limit permissions per resource and per tool call.
- Don’t let the language model decide authorization. Auth0 stresses that every agent action must be explicitly authorized outside the LLM.
- Log everything. Ideally, logs include user intent, agent identity, tool calls, input context, authorization decisions, side effects, and results.
- Monitor agent behavior in real time, and enforce policies as close to the action as possible.
Okta describes the rules of the game clearly. Access is granted only if the agent’s identity is verified, human authorization is active, and the action is within scope. Risk signals are also checked at that moment, before the agent continues its task.
Companies don’t need to wait for specialized products to get started. Auditing data permissions before turning on an agent is an inexpensive first step. From there, Zero Trust for AI agents can be built up in stages, starting with low-risk agents and working toward those that hold sensitive access.
Get the latest information and more useful articles only at bacatulisan.com